

SC-401 Certification Overview - [Sep 11, 2026] Latest SC-401 PDF Dumps
The Best Microsoft SC-401 Study Guides and Dumps of 2026
NEW QUESTION # 60
You have a Microsoft 365 tenant.
You have a database that stores customer details. Each customer has a unique 13-digit identifier that consists of a fixed pattern of numbers and letters.
You need to implement a data loss prevention (DLP) solution that meets the following requirements:
*Email messages that contain a single customer identifier can be sent outside your company.
*Email messages that contain two or more customer identifiers must be approved by the company's data privacy team.
Which two components should you include in the solution? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. a sensitivity label
- B. a sensitive information type
- C. a DLP policy
- D. a retention label
- E. a mail flow rule
Answer: B,C
Explanation:
You need to define a custom sensitive information type that recognizes the unique 13-digit identifier format for customer records. Microsoft Purview DLP policies use these types to identify and protect sensitive data.
A Data Loss Prevention (DLP) policy is required to enforce the rules. It will allow emails with a single identifier but trigger an approval workflow when two or more identifiers are detected.
NEW QUESTION # 61
You need to meet the technical requirements for the confidential documents.
What should you create first, and what should you use for the detection method? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.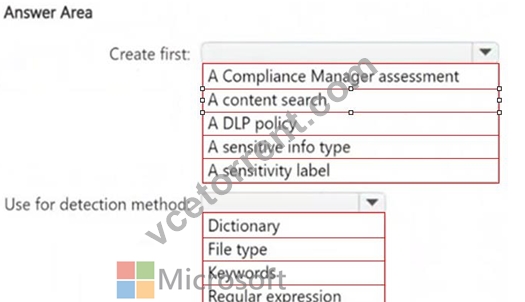
Answer:
Explanation: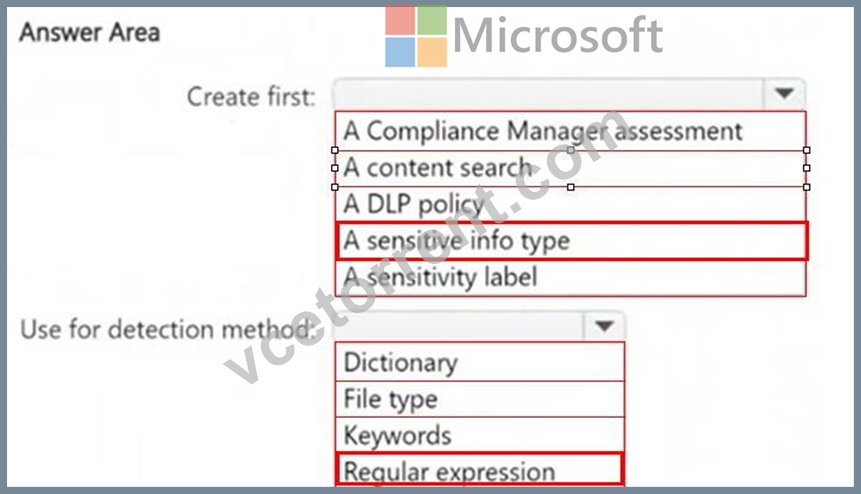
NEW QUESTION # 62
You have a Microsoft 365 E5 subscription that contains a user named User1. The subscription contains an Endpoint data loss prevention (Endpoint DLP) policy as shown in the Actions exhibit. (Click the Actions tab.)
You configure the Upload to a restricted cloud service domain or access from an unallowed browsers settings as shown in the Upload restrictions exhibit. (Click the Upload restrictions tab.)
You configure the Paste to supported browsers settings as shown in the Paste restrictions exhibit. (Click the Paste restrictions tab.)
When User1 pastes content into ChatGPT, the user receives the error message shown in the Error exhibit.
(Click the Error tab.)
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE; Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
NEW QUESTION # 63
You have a Microsoft 365 E5 subscription.
You plan to use Microsoft Purview insider risk management.
You need to create an insider risk management policy that will detect data theft from Microsoft SharePoint Online by users that submitted their resignation or are near their employment termination date.
What should you do first?
- A. Configure a HR data connector.
- B. Configure a Physical badging connector.
- C. Configure Office indicators.
- D. Onboard devices to Microsoft Defender for Endpoint.
Answer: A
NEW QUESTION # 64
You have a Microsoft 365 subscription. Auditing is enabled.
A user named User1 is a member of a dynamic security group named Group1.
You discover that User1 is no longer a member of Group1.
You need to search the audit log to identify why User1 was removed from Group1.
Which two activities should you use in the search? To answer, select the appropriate activities in the answer area.
NOTE: Each correct selection is worth one point.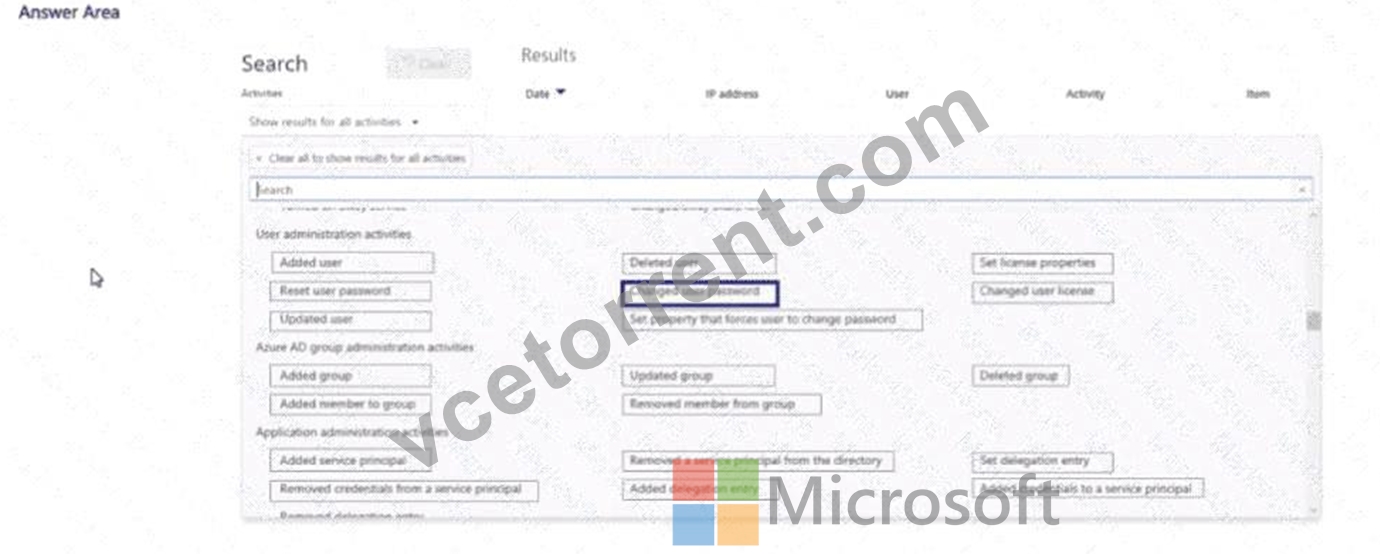
Answer:
Explanation: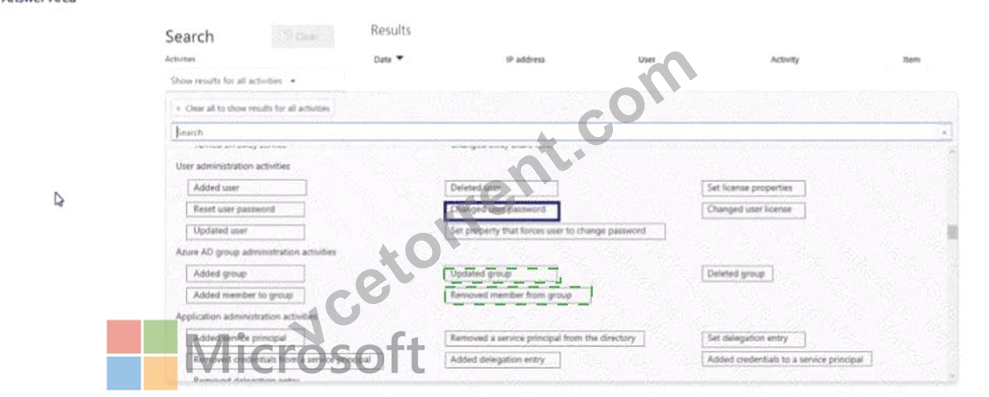
Explanation:
NEW QUESTION # 65
Hotspot Question
You have a Microsoft 365 E5 subscription that contains the data loss prevention (DLP) policies shown in the following table.
You have a custom employee information form named Template1.docx.
You plan to create a sensitive info type named Sensitive1 that will use the document fingerprint from Template1.docx.
What should you use to create Sensitive1, and in which DLP policies can you use Sensitive1? To answer, select the appropriate options in the answer area.
Answer:
Explanation:
Explanation:
Box 1: Microsoft Purview portal
Box 2: DLP1, DLP2, and DLP3
DLP can use document fingerprinting as a detection method in Exchange, SharePoint, OneDrive, Teams, and Devices.
Reference:
https://learn.microsoft.com/en-us/purview/sit-document-fingerprinting
NEW QUESTION # 66
You need to test Microsoft Purview Advanced Message Encryption capabilities for your company.
The test must verify the following information:
- The acquired default template names
- The encryption and decryption verification status
Which PowerShell cmdlet should you run?
- A. Test-ClientAccessRule
- B. Test-OAuthConnectivity
- C. Test-IRMConfiguration
- D. Test-Mailflow
Answer: C
Explanation:
Verify Microsoft Purview Message Encryption configuration in Exchange Online PowerShell You can verify that your Microsoft 365 tenant is properly configured to use Microsoft Purview Message Encryption in Exchange Online PowerShell.
1. Using a work or school account that has sufficient permissions in your organization, such as Compliance Administrator, start a Windows PowerShell session and connect to Exchange Online.
For instructions, see Connect to Exchange Online PowerShell.
2. Run the Get-IRMConfiguration cmdlet.
You should see a value of $True for the AzureRMSLicensingEnabled parameter, which indicates that Microsoft Purview Message Encryption is configured in your tenant. If it is not, use Set- IRMConfiguration to set the value of AzureRMSLicensingEnabled to $True to enable Microsoft Purview Message Encryption.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/set-up-new-message-encryption-capabilities
NEW QUESTION # 67
You have a Microsoft 365 tenant.
You have a database that stores customer details. Each customer has a unique 13-digit identifier that consists of a fixed pattern of numbers and letters.
You need to implement a data loss prevention (DLP) solution that meets the following requirements:
- Email messages that contain a single customer identifier can be sent
outside your company.
- Email messages that contain two or more customer identifiers must be
approved by the company's data privacy team.
Which two components should you include in the solution? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. a sensitivity label
- B. a sensitive information type
- C. a DLP policy
- D. a retention label
- E. a mail flow rule
Answer: B,C
Explanation:
You need to define a custom sensitive information type that recognizes the unique 13-digit identifier format for customer records. Microsoft Purview DLP policies use these types to identify and protect sensitive data.
A Data Loss Prevention (DLP) policy is required to enforce the rules. It will allow emails with a single identifier but trigger an approval workflow when two or more identifiers are detected.
NEW QUESTION # 68
You have a Microsoft 365 subscription that contains two Microsoft SharePoint Online sites named Site1 and Site2. You plan to use policies to meet the following requirements:
* Add a watermark of Confidential to a document if the document contains the words Project1 or Project2.
* Retain a document for seven years if the document contains credit card information.
* Add a watermark of Internal Use Only to all the documents stored on Site2.
* Add a watermark of Confidential to all the documents stored on Site1.
You need to recommend the minimum number of sensitive info types required.
How many sensitive info types should you recommend?
- A. 0
- B. 1
- C. 2
- D. 3
Answer: B
NEW QUESTION # 69
You have a Microsoft 365 E5 subscription that contains the devices shown in the following table.
You are evaluating Microsoft Purview Information Protection.
On which devices can you deploy the Information Protection client?
- A. Device1 only
- B. Device1, Device2, and Device3 only
- C. Device1 and Device2 only
- D. Device1, Device2, Device3, and Device4
- E. Device1, Device3, and Device4 only
Answer: C
Explanation:
The following operating systems support the Microsoft Purview Information Protection client:
Windows 11, including Windows 11 Enterprise multi-session
Windows 10 (x64) (Handwriting isn't supported in the Windows 10 RS4 build and later) Windows Server 2019 Windows Server 2016 ARM64 is supported for the viewer and file labeler, but isn't supported for the scanner or PowerShell Incorrect:
[Not Device 3, Not Device4]
The full Microsoft Purview Information Protection (MIP) client (for both labeling/protection and viewing) is primarily for Windows. For macOS and Android devices, users can generally view protected content using specific apps or built-in Office app capabilities, but dedicated functionality for applying new labels and protection might be different.
Reference:
https://learn.microsoft.com/en-us/purview/information-protection-client
NEW QUESTION # 70
SIMULATION
Username and password
Use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and select the username below.
To enter your password, place your cursor in the Enter password box and select the password below.
Microsoft 365 Username:
[email protected]
Microsoft 365 Password: XXXXXXXXX
If the Microsoft Edge browser or Microsoft 365 portal does not load successfully, select the Microsoft Edge browser icon from the task bar, type the URL "https://admin.microsoft.com", and press Enter.
The following information is for technical support purposes only:
Lab Instance: XXXXXXXXX
Task 8
You need to ensure that the Employee Records retention label is applied automatically to content that meets the following requirements:
- Contains only the U.K. Unique Taxpayer Reference Number sensitive info type
- Is located in any Exchange email, SharePoint sites, OneDrive accounts or Microsoft 365 groups
Answer:
Explanation:
See explanation below.
Explanation:
To configure a retention label to use a specific sensitive information type, you need to create an auto-labeling policy in the Microsoft Purview portal that applies a label to content containing that sensitive information type. First, create the retention label itself with its retention settings, and then create the auto-labeling policy, select "Apply label to content that contains sensitive info," choose the desired sensitive info type, specify the locations to apply it, and select your retention label.
Step 1: Sign in to the Microsoft Purview portal.
Step 2: If you're using records management [Yes!]: Solutions > Records Management > Policies > Label policies > Auto-apply a label Step 3: Enter a name and description for this auto-labeling policy, and then select Next.
Step 4: For Choose the type of content you want to apply this label to, select one of the available conditions.
Auto-apply labels to content with specific types of sensitive information Step 5: Select U.K. Unique Taxpayer Reference Number sensitive info type in the U.K Personally Identifiable Information (PII) Data template.
When you create auto-apply retention label policies for sensitive information, you see the same list of policy templates as when you create a Microsoft Purview Data Loss Prevention (DLP) policy. Each template is preconfigured to look for specific types of sensitive information. In the following example, the sensitive info types are from the Privacy category, and U.S Personally Identifiable Information (PII) Data template:
Step 6: For the Assign admin units page, keep the default of Full directory. Currently, admin units aren't supported for this policy.
Step 7: For the Choose the type of retention policy to create page, select Adaptive or Static.
[Select Static]
Step 8: If you chose Static: On the Choose locations page, toggle on or off any of the locations.
Select:
Exchange email
SharePoint sites
OneDrive accounts
Microsoft 365 groups
Step 9: Follow the prompts to select a retention label, whether to run the policy in simulation mode or turn it on (if applicable for your chosen condition), and then review and submit your configuration choices.
Reference:
https://learn.microsoft.com/en-us/purview/apply-retention-labels-automatically
https://learn.microsoft.com/en-us/purview/retention-settings#locations
NEW QUESTION # 71
HOTSPOT
You have a Microsoft 365 E5 subscription that uses Microsoft Purview.
You need ensure that an incident will be generated when a user visits a phishing website.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation: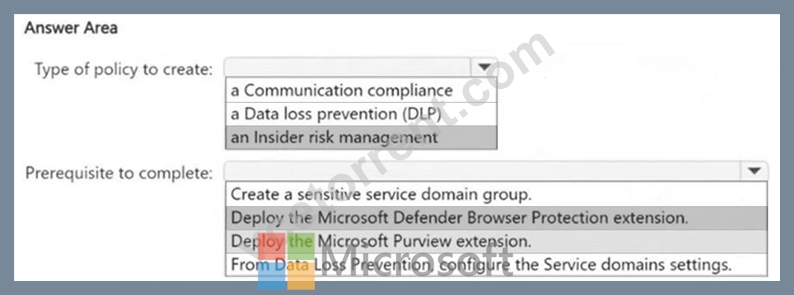
Box 1: Insider Risk Management policies in Microsoft Purview can be configured to detect risky behavior, such as accessing phishing websites. These policies monitor user activity, generate alerts, and help organizations investigate potential security threats.
Box 2: Microsoft Defender Browser Protection extension helps in detecting unsafe or phishing websites and integrating this detection with Insider Risk Management policies. This extension works with Microsoft Edge and Google Chrome to identify risky browsing activity and trigger alerts.
NEW QUESTION # 72
How many files in Site2 can User1 and User2 access after you turn on DLPpolicy1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 73
You have a Microsoft 365 E5 tenant that has devices onboarded to Microsoft Defender for Endpoint as shown in the following table.
You plan to start using Microsoft 365 Endpoint data loss protection (Endpoint DLP).
Which devices support Endpoint DLP?
- A. Device1 only
- B. Device1 and Device2 only
- C. Device1, Device2, Device3, and Device4
- D. Device1, Device2, and Device4 only
- E. Device1 and Device4 only
Answer: B
Explanation:
Microsoft 365 Endpoint data loss prevention (Endpoint DLP) is supported only on Windows 10 and Windows
11 devices. It does not support macOS or iOS at this time.
From the provided table:
# Device1 (Windows 11) - Supported
# Device2 (Windows 10) - Supported
# Device3 (iOS) - Not supported
# Device4 (macOS) - Not supported
Thus, only Device1 and Device2 support Endpoint DLP.
NEW QUESTION # 74
You have a Microsoft 36S subscription that contains the sensitive information types (SITs) shown in the following exhibit.
Use the drop-down menus To select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct flection is worth one point.
Answer:
Explanation:
Explanation:
NEW QUESTION # 75
You have a Microsoft 365 subscription. Auditing is enabled.
A user named User1 is a member of a dynamic security group named Group1.
You discover that User1 is no longer a member of Group1.
You need to search the audit log to identify why User1 was removed from Group1.
Which two activities should you use in the search? To answer, select the appropriate activities in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation: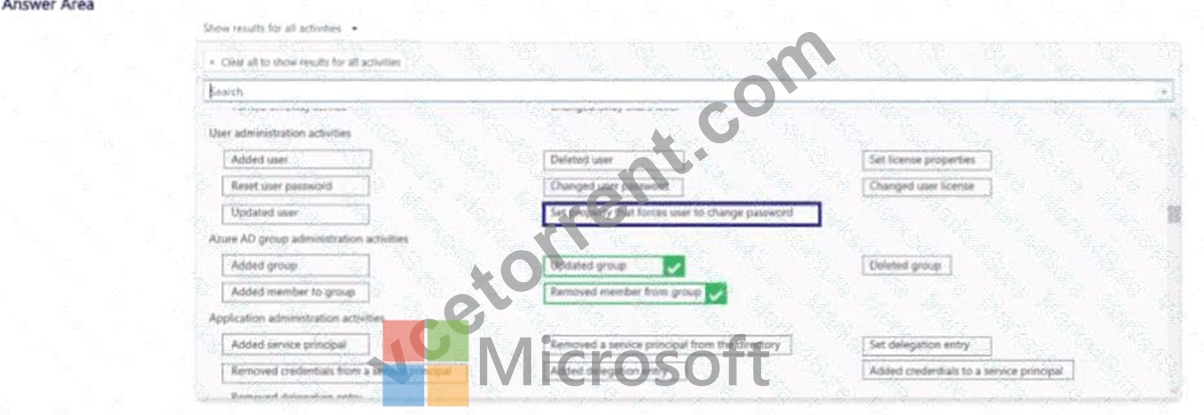
NEW QUESTION # 76
You have a Microsoft 36S ES subscription
You need to implement Endpoint data loss prevention (Endpoint DLP) to meet the following requirements:
* Ensure that users can upload data to only two sites named Site1 and Site2.
* Prevent users from pasting data to two search engines named Search1 and Search2.
* Minimize the number of policies and groups.
What If the minimum number of sensitive service domain groups and Endpoint DIP policies required? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
NEW QUESTION # 77
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You recently discovered that the developers at your company emailed Azure Storage Account keys in plain text to third parties.
You need to ensure that when Azure Storage Account keys are emailed, the emails are encrypted.
Solution: You create a data loss prevention (DLP) policy that has only the Exchange email location selected.
Does this meet the goal?
- A. Yes
- B. No
Answer: A
Explanation:
To ensure Azure Storage Account keys are encrypted when sent via email, you need a Data Loss Prevention (DLP) policy that detects Azure Storage Account keys using a sensitive information type and automatically encrypts emails containing these keys.
A DLP policy with Exchange email as the only location meets this requirement because it identifies sensitive data in email messages and it applies protection actions, such as encryption, blocking, or alerts.
NEW QUESTION # 78
You have a Microsoft 36S ES subscription.
You need to create the Microsoft Purview insider risk management policies shown in the following table.
Which policy template should you use for each policy? To answer, drag the appropriate policy templates to the correct polices Each template may be used once more than once or not at all. You may need to drag the split bar between panes or scroll to view..
Answer:
Explanation:
Explanation:
NEW QUESTION # 79
You have a Microsoft 365 subscription.
You identify the following data loss prevention (DLP) requirements:
* Send notifications to users if they attempt to send attachments that contain an EU Social Security Number (SSN) or Equivalent ID.
* Prevent any email messages that contain credit card numbers from being sent outside your organization.
* Block the external sharing of Microsoft OneDrive content that contains EU passport numbers.
* Send administrators email alerts if any rule matches occur.
What is the minimum number of DLP policies and rules you must create to meet the requirements? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.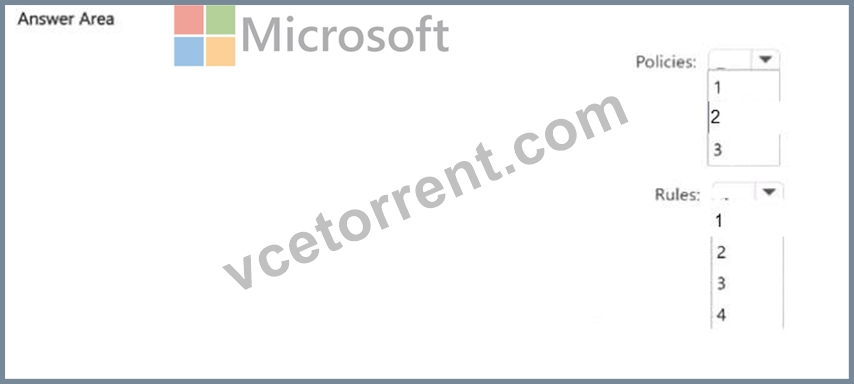
Answer:
Explanation:
Explanation:
NEW QUESTION # 80
You need to create a trainable classifier that can be used as a condition in an auto-apply retention label policy.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.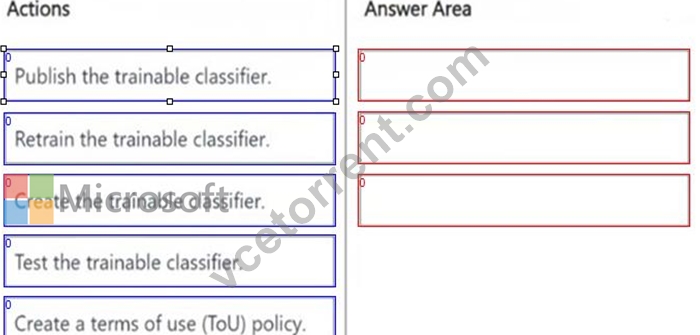
Answer:
Explanation:
NEW QUESTION # 81
You have a Microsoft 36515 subscription tha1 contains a Microsoft SharePoint Online site named Site1 Site1 contains three tiles named File1. File2 and File3.
You create the data loss prevention (DIP) policies shown in the following table.
The DIP rule matches for each tile are shown in the following table.
How many DIP policy matches events will be added to Activity explorer, and how many policy matches will be added to the DLP incidents report? To answer, select the appropriate options m the answer area.
Answer:
Explanation:
Explanation:
Activity Explorer logs a DLP rule match event each time any DLP rule condition is met on a file.
File1 matches Rule11 and Rule12 # 2 events
File2 matches Rule21 and Rule22 # 2 events
File3 matches Rule11 and Rule22 # 2 events
Total events in Activity Explorer = 2 + 2 + 2 = 6.
Microsoft notes that Activity explorer shows granular DLP activities such as policy rule matches per item.
The DLP incidents report aggregates by policy match per item, not by each rule in that policy. Multiple rules from the same policy on the same item count as one incident; if different policies match the same item, each policy creates its own incident.
File1: Rules from DLP1 only # 1 incident
File2: Rules from DLP2 only # 1 incident
File3: One rule from DLP1 and one from DLP2 # 2 incidents
Total incidents = 1 + 1 + 2 = 4.
References: Microsoft Purview DLP explains that Activity explorer records detailed DLP activities, while DLP incidents are created when a policy match occurs for an item, and multiple rule matches within a single policy are consolidated into a single incident for that item.
NEW QUESTION # 82
XYZ needs to assign permissions to compliance officers so they can create and manage Data Loss Prevention (DLP) policies but prevent other users from altering these settings. Which permission level should be assigned?
- A. Compliance Administratorright
- B. Exchange Admin
- C. Security Reader
- D. Global Administrator
Answer: A
Explanation:
This role is specifically designed to manage compliance features, including creating and managing DLP policies. It provides the necessary permissions for compliance officers to handle DLP settings without giving them broader administrative rights.
Reference:
https://learn.microsoft.com/en-us/purview/dlp-create-deploy-policy?tabs=purview#permissions
NEW QUESTION # 83
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You recently discovered that the developers at your company emailed Azure Storage Account keys in plain text to third parties.
You need to ensure that when Azure Storage Account keys are emailed, the emails are encrypted.
Solution: You configure a mail flow rule that matches a sensitive info type.
Does this meet the goal?
- A. Yes
- B. No
Answer: B
Explanation:
To ensure Azure Storage Account keys are encrypted when sent via email, you need a Data Loss Prevention (DLP) policy that detects Azure Storage Account keys using a sensitive information type and automatically encrypts emails containing these keys.
Mail flow rules (transport rules) can detect sensitive info, but they are limited in encryption capabilities.
DLP policies provide more advanced protection and integration with Microsoft Purview for sensitive info detection.
NEW QUESTION # 84
You have a Microsoft 36S ES subscription that contains two Windows devices named Devicel1and Device2 Device1 has the default browser set to Microsoft Edge. Devke2 has the default browser set to Google Chrome.
You need to ensure that Microsoft Purview insider risk management can collect signals when a user copies files to a USB device by using their default browser.
What should you deploy to each device? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Step 1 - Scenario
The requirement is to ensure Microsoft Purview Insider Risk Management can collect signals when a user copies files to a USB device using their default browser. The devices differ by browser type:
Device1 # Default browser = Microsoft Edge
Device2 # Default browser = Google Chrome
Step 2 - Signal collection methods in Insider Risk Management
Insider Risk Management uses Microsoft Purview Information Protection client and Purview browser extensions to collect activity signals.
For Microsoft Edge (Chromium-based), insider risk signals are collected via the Microsoft Purview Information Protection client.
For Google Chrome, signals are collected through the Microsoft Purview extension (available in the Chrome Web Store).
The Microsoft Defender Browser Protection extension is for web protection against malicious sites, not for insider risk activity signals, so it is irrelevant here.
Step 3 - Microsoft Reference
Microsoft documentation:
"For insider risk signals collection in Microsoft Edge, the Microsoft Purview client must be deployed. For Google Chrome, the Microsoft Purview extension is required." Reference: Insider risk management activity signals
NEW QUESTION # 85
......
Microsoft SC-401 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
Valid SC-401 Exam Updates - 2026 Study Guide: https://www.vcetorrent.com/SC-401-valid-vce-torrent.html
Top Microsoft SC-401 Exam Audio Study Guide! Practice Questions Edition: https://drive.google.com/open?id=1xVQ484L7NR6O04uvk8aq6nazOgDMznZP